Device: GL-E5800 (Mudi 7) Firmware: 4.10.0 (release) — also reproduced on 4.10.0 beta2 Not affected: 4.8.5 (release)
Summary
After changing the LAN IP away from the default, the router creates a firewall rule named Block-LAN-mgmt-guest with src='lan' instead of src='guest'. This REJECTs all traffic from LAN clients to the router's own management ports, making the web admin panel and LuCI completely unreachable. SSH (port 22) still works and is the only way back in.
This happens even though the guest network is disabled and cannot be enabled.
Steps to reproduce
-
Flash 4.10.0, do not keep settings
-
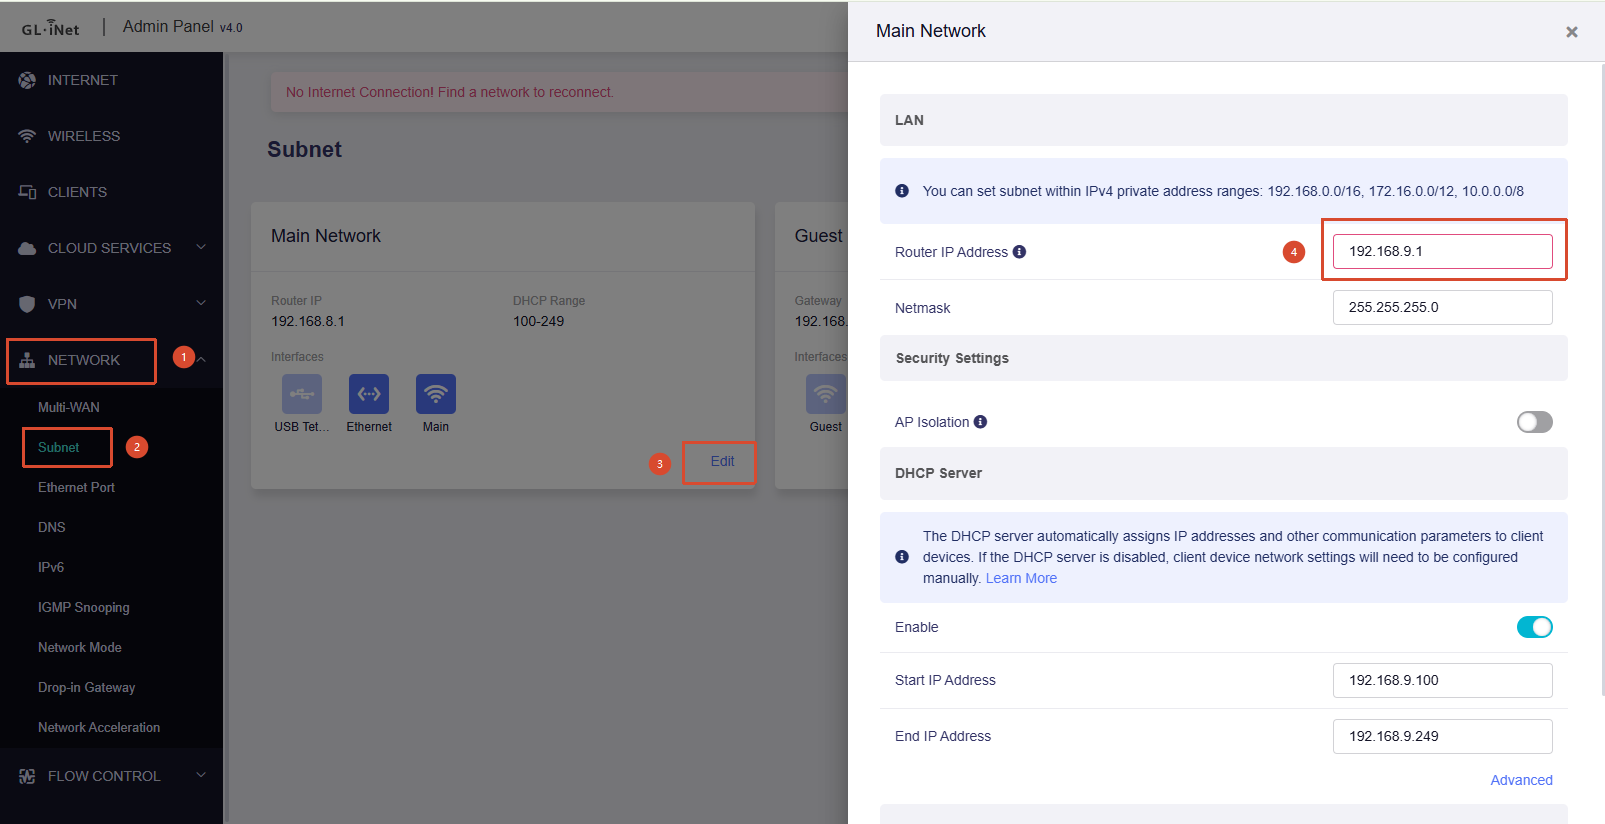
Go to NETWORK → LAN and change the LAN IP from
192.168.8.1to192.168.9.1 -
Reconnect, then try to open
http://192.168.9.1
Expected: admin panel loads Actual: ERR_CONNECTION_REFUSED on 80, 443, 8080 and 8443. SSH still works.
Root cause
network.guest.ipaddr is set to the same address as the LAN:
root@GL-E5800:~# uci show network | grep -E "\.ipaddr="
network.lan.ipaddr='192.168.9.1'
network.guest.ipaddr='192.168.9.1'      <-- identical to LAN
...

root@GL-E5800:~# uci show network | grep -i "guest.disabled"
network.guest.disabled='1'
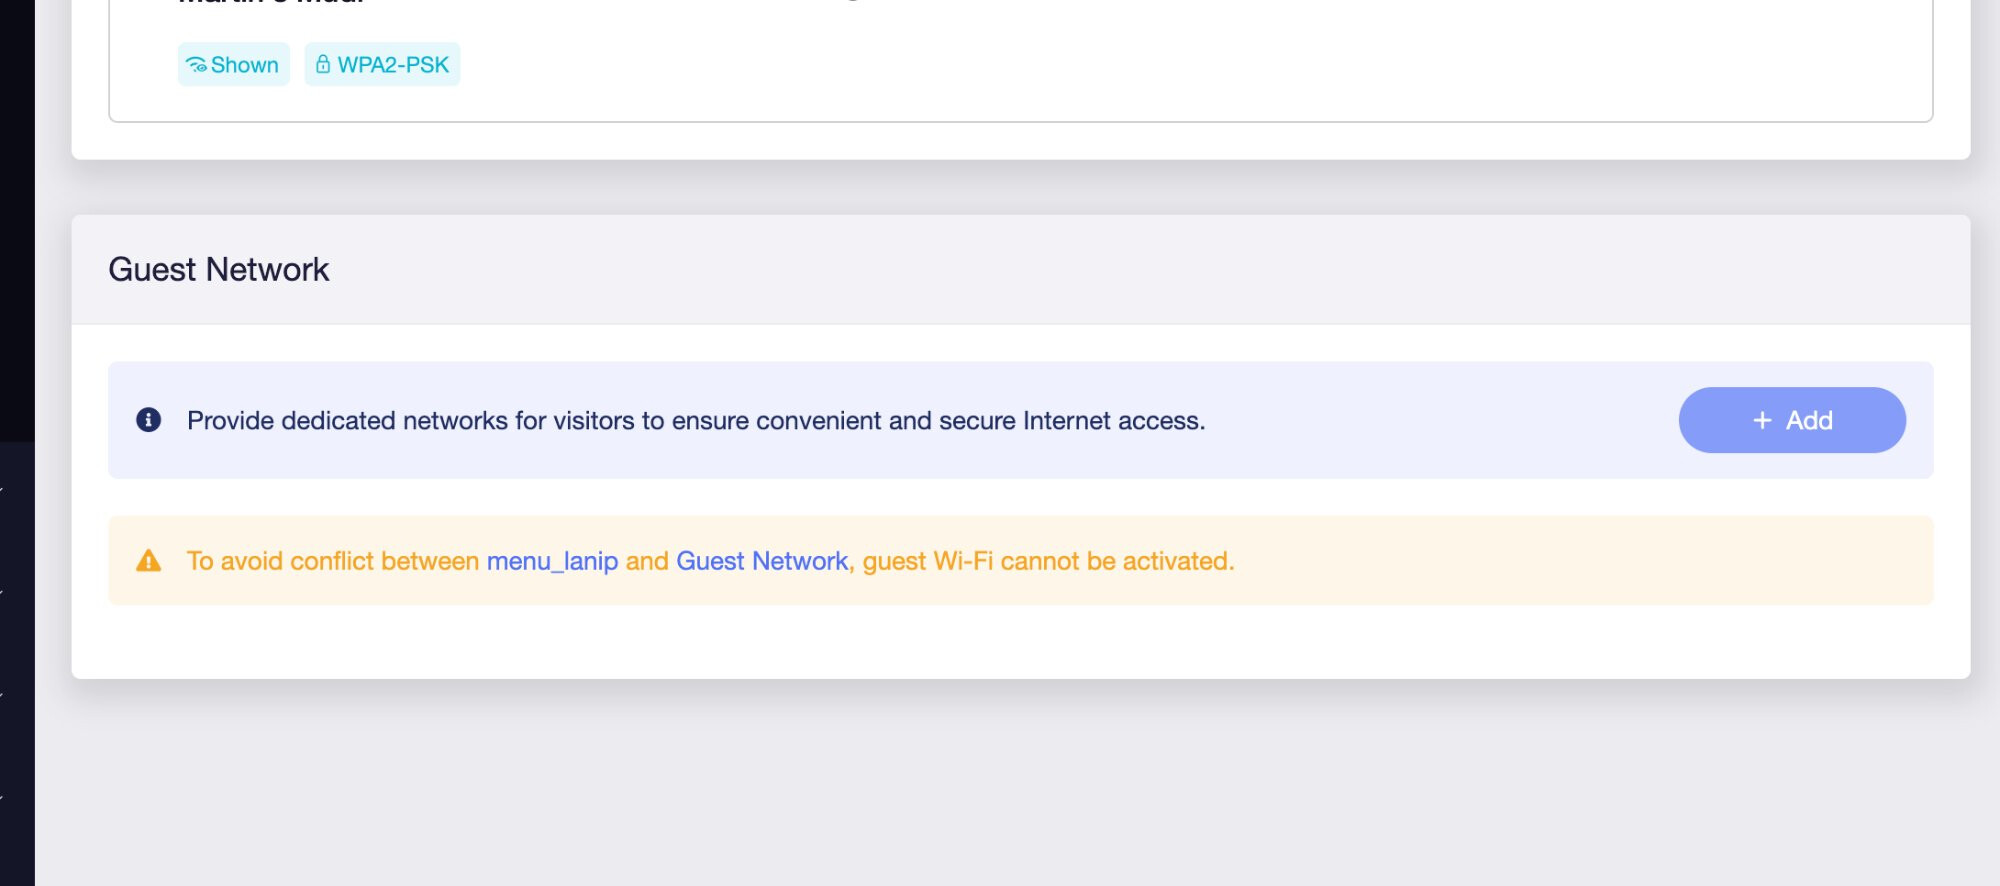
The guest network is therefore disabled (the UI shows "To avoid conflict between menu_lanip and Guest Network, guest Wi-Fi cannot be activated" — note menu_lanip is an untranslated i18n key leaking into the UI), but the firewall rule is still generated, and with the wrong zone:
root@GL-E5800:~# uci show firewall.@rule[14]
firewall.cfg2192bd=rule
firewall.cfg2192bd.name='Block-LAN-mgmt-guest'
firewall.cfg2192bd.src='lan'                      <-- should be 'guest'
firewall.cfg2192bd.dest_ip='192.168.9.1'
firewall.cfg2192bd.proto='tcp udp'
firewall.cfg2192bd.dest_port='80 443 8080 8443'
firewall.cfg2192bd.target='REJECT'
Which lands in the input_lan chain and rejects the admin's own traffic:
root@GL-E5800:~# nft list chain inet fw4 input_lan | grep Block-LAN
  ip daddr 192.168.9.1 tcp dport { 80, 443, 8080, 8443 } counter packets 14 bytes 896 \
    jump handle_reject comment "!fw4: Block-LAN-mgmt-guest"
  ip daddr 192.168.9.1 udp dport { 80, 443, 8080, 8443 } counter packets 0 bytes 0 \
    jump handle_reject comment "!fw4: Block-LAN-mgmt-guest"
(The packet counter is my own browser attempts. nginx is listening normally on 0.0.0.0:80 and :443 — this is purely a firewall issue.)
Workaround
sh
uci set firewall.@rule[14].src='guest'
uci commit firewall
/etc/init.d/firewall reload
Verified: the rule moves out of input_lan into input_guest, the admin panel becomes reachable again, and the original intent (blocking guests from the management UI) is preserved.
Suggested fixes
-
Block-LAN-mgmt-guestshould always be created withsrc='guest' -
Do not create the rule at all when
network.guest.disabled='1' -
Changing the LAN IP should not copy that address onto
network.guest.ipaddr— pick a non-overlapping subnet instead -
Fix the untranslated
menu_lanipstring in the Guest Network warning
Impact
A user who changes the LAN IP and does not know the root@ SSH trick has no path back into the router short of a factory reset or U-Boot reflash. On a travel router this can happen away from home.