So for client devices when i want to keep the ip i am currently at and access my homelab i can simply route only DNS traffic by setting AllowedIPs to the dns ip and the homelab where the wireguard server is running. I don’t know how to do this on my Beryl 7. No matter what i try the gl inet vpn client will not use the DNS server ip in the client config. What should my settings look like to make this work?
The only thing that works is setting the target to my homelab domain and that will cause the vpn to use the dns server only on my homelab domain. I want it to use the dns server on ALL the web traffic.
Hi,
You can achieve this by routing your remote DNS server and homelab subnet through the WireGuard tunnel, while allowing all other traffic to continue using the local WAN.
Please try the following configuration:
-
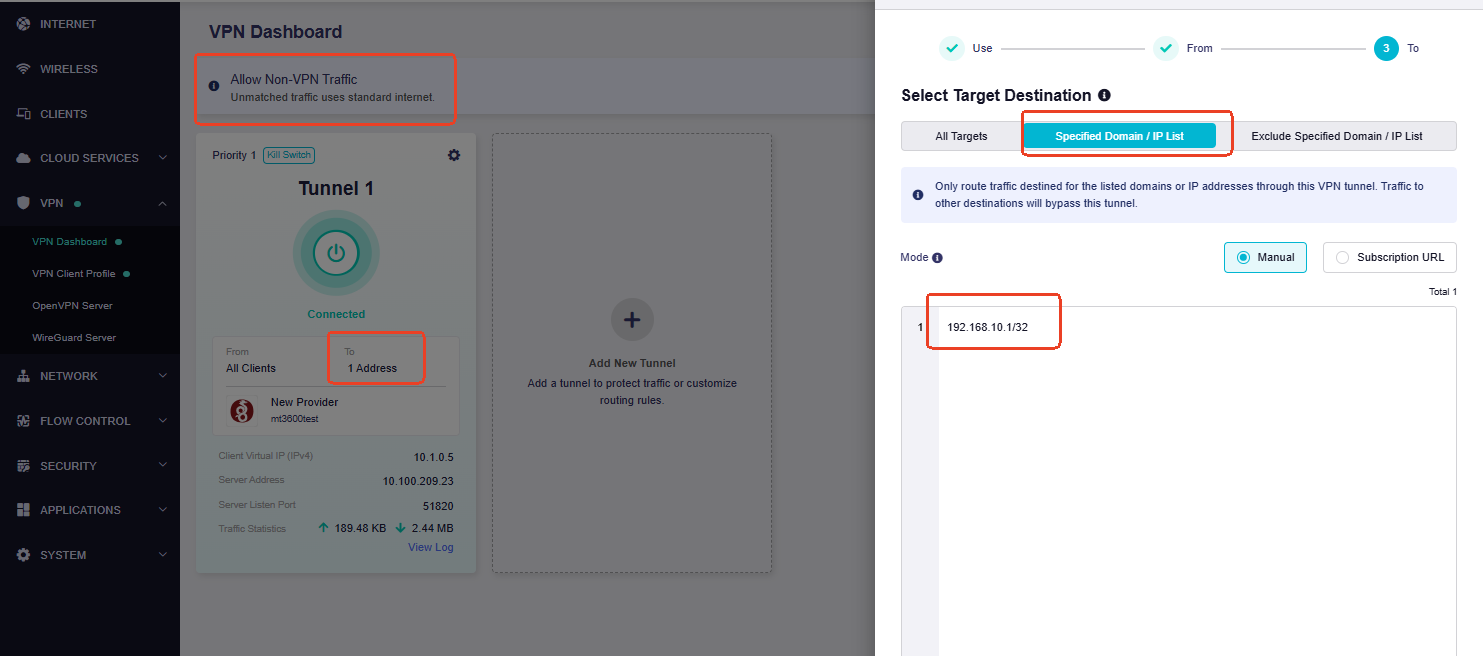
Go to VPN → VPN Dashboard , and add or edit the WireGuard tunnel, under To , select Specified Domain / IP List , then add the IP address of your remote DNS server and make sure Allow Non-VPN Traffic is enabled so that traffic which does not match the above destinations continues to use the local WAN.
For example: 192.168.10.1/32
-
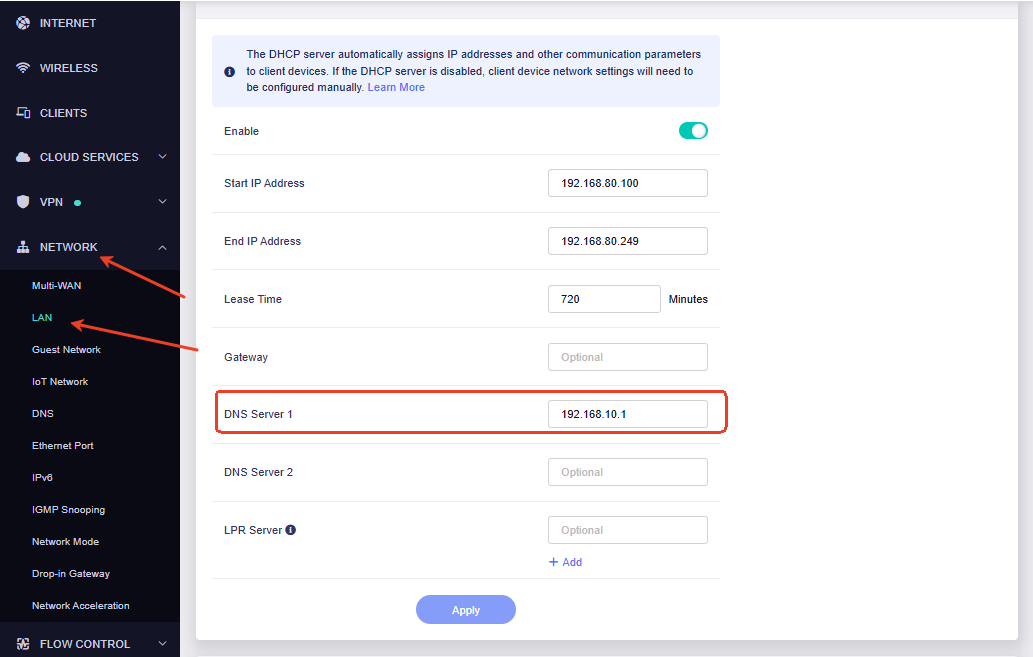
Go to Network → LAN → DHCP Server → Advanced , and enter the remote DNS server IP in DNS Server 1 .
After applying the settings, reconnect the client devices to the router so that they can obtain the updated DNS settings through DHCP.
With this configuration, DNS queries from the clients will be sent to the remote DNS server through the WireGuard tunnel, while other Internet traffic will continue to use the local WAN connection.
Thank you for your support.
I have tested it and this works. However i would like this to work with turning my vpn server on and off without manually changing the DHCP dns server everytime. Is that possible.
Hi,
In this case, you can try using both DNS fields in the LAN DHCP settings.
Please keep DNS Server 1 set to your remote/HomeLab DNS server, which is already routed through the WireGuard tunnel, and set DNS Server 2 to a normal DNS server that remains reachable when the VPN server is offline.
For example:
- DNS Server 1: your HomeLab DNS server
- DNS Server 2: your Beryl 7 LAN IP or another normal DNS server
With this setup, when the VPN and remote DNS are available, the client should normally use DNS Server 1. If the remote DNS becomes unavailable, the client may fall back to DNS Server 2.
Please note that DNS failover behavior is handled by the client operating system, so the exact switching behavior and timing may vary between different devices.