Maybe I was confused, but I could have sworn I read @will.qiu saying AP isolation only works for wireless and not wired clients.
When manually setting the WiFi channels, as long as they're different channels, it should minimize any chance of interference. Are there any devices or apps to help determine the best channel to use for 2.4, 5, and 6 GHz? How close is too close in terms of distance? Does it even matter if the APs are using different channels?
My ISP's access point is fairly locked down, so there aren't a lot of settings I can change. The reason why I need your help to get this to work with the Brume 3 is because the specs of the access point are impressive. It has the following: Antennas: 2.4GHz 4x4 | 5GHz 1 4x4 | 5GHz 2 4x4. My biggest worry is privacy and security. Since my ISP’s access point is connected to the Brume 3, all privacy and security will start and end with the Brume 3, right? For example, even if my ISP abandons firmware updates for the access point, it won't be an issue, as everything is routed through the Brume 3. Besides what you have described in your posts to set up my network, is there anything more to enhance the privacy and security of my network? Data leaking to the wider internet and/or a backdoor to my ISP is a concern, but if you tell me the Brume 3 will protect me, then I'll take you at your word.
Thanks for your follow-up questions. We would like to clarify a few points.
The isolation mentioned here is network isolation between AP1 and AP2, not AP/client isolation within the same AP. With AP1 and AP2 connected to different LAN ports on the Brume 3 and assigned to different subnets, Brume 3 can control traffic between these two networks through firewall rules. However, devices connected to the same AP/network can still communicate with each other unless client isolation is enabled on the AP.
About Wi-Fi stability with two APs
There is no fixed distance requirement between two APs. The main factors are channel overlap, signal strength, and interference from nearby Wi-Fi networks.
You can use a Wi-Fi analyzer app to check nearby Wi-Fi networks, signal strength, and channel usage, then select less congested channels for each AP.
For example, avoid using the same channel for both APs when their coverage areas overlap.
In this case, the Brume 3 becomes the main router and manages DHCP, routing, firewall rules, and isolation between the AP1 and AP2 networks.
With proper firewall rules, devices connected to AP1 will not be able to directly access devices connected to AP2, and vice versa. However, this does not mean the Brume 3 can fully protect the AP itself. The security of each AP still depends on its own firmware, configuration, and security updates.
For example, if an AP itself has a security issue, devices within that same AP/network may still be affected.
My access point doesn't have the option to do client isolation. I don't know for sure if my ISP's access point properly configured its guest network to isolate all clients from each other. Is there anything I can do with the Brume 3 to isolate all connected clients within the same access point?
Since the Brume 3 only has two LAN ports, if I connect a switch to the Brume’s LAN port, how do I isolate traffic for each LAN port on the switch? For example, can the access point's wireless clients in switch LAN1 be isolated from a wired client in LAN2? Is this configured on the switch or can this be done with a Brume 3? What kind of switch is best for this situation?
If your ISP AP does not provide a Client Isolation option, you can first check whether its Guest network enables this function by default.
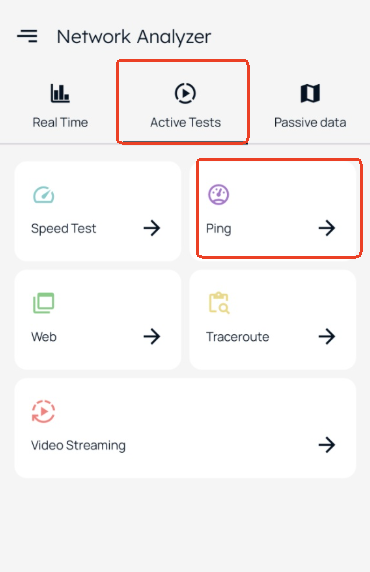
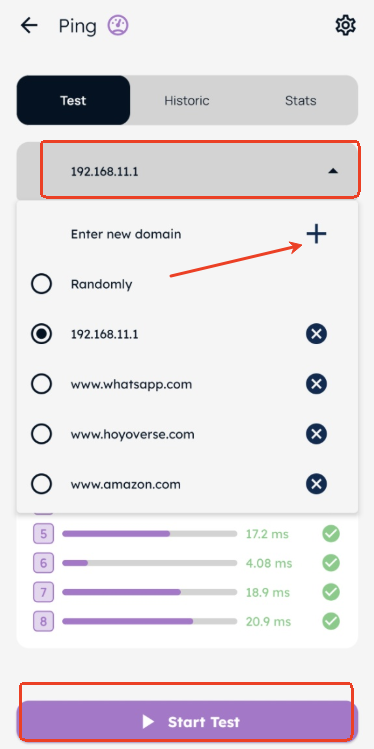
You can connect two devices to the same Guest SSID and try to ping each device’s local IP address from the other device.
If the devices cannot communicate on the Guest network, the Guest network is likely applying client isolation.
If they can still communicate with each other on the Guest network, the Guest network does not provide complete client isolation.
Brume 3 cannot isolate wireless clients connected to the same AP, SSID, and subnet, because this traffic is normally forwarded locally by the AP and does not pass through the Brume 3 firewall.
If the Guest network does not isolate clients and you require this function, we recommend using an AP that explicitly supports Client Isolation or AP Isolation.
However, please note that client isolation prevents local communication between connected devices.
Features such as AirPlay, network printing, screen casting, and smart-home control normally use local broadcast or multicast protocols, such as Bonjour/mDNS, to discover nearby devices before establishing a local connection.
When Client Isolation is enabled, these discovery packets or the subsequent direct connection between the devices may be blocked.
Internet access should still work normally, but local device discovery and device-to-device communication may not work.
For devices connected through a switch, we recommend using a Layer 2 managed switch that supports IEEE 802.1Q VLANs.
The managed switch is responsible for assigning its physical ports to different VLANs. The managed switch separates the physical ports into different VLANs, while Brume 3 provides the gateways and enforces the traffic rules between those VLANs.
In this setup, the wireless clients behind the AP connected to switch LAN1 can be isolated from the wired client connected to LAN2.
For example, configure LAN1 as an access port for VLAN 10 and LAN2 as an access port for VLAN 20 on the managed switch.
The switch port connected to Brume 3 should be configured as a tagged/trunk port carrying both VLANs.
On Brume 3, create a separate network interface and firewall zone for each VLAN. Both VLANs can be allowed to access the Internet, while forwarding between the two firewall zones remains blocked.This isolates the AP network on LAN1 from the wired client on LAN2.
You can use the same ping test for devices connected to the same network.
If client isolation is enabled, the ping should fail; otherwise, devices in the same subnet can normally communicate with each other directly.
I have received your private message and need take some time to review the information and understand the configuration.
Maybe there is something that I don't understand about this forum, but sometimes when I try to quote your message, it doesn't seem to tag you. Sometimes it does. Why?
Anyways, can I do the ping test with an iPhone and Android connected to the WiFi network? If so, how?
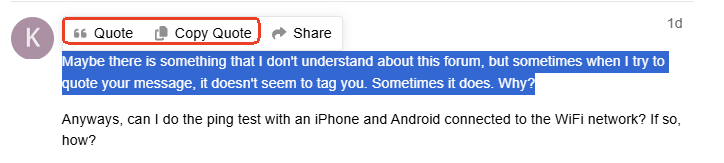
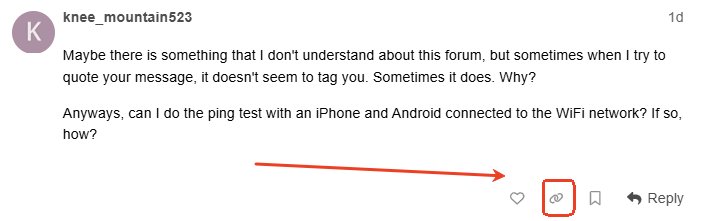
You can select the text in my post and click Quote \ copy Quote , or click the link icon below the post to copy its link and paste it into the reply box.