Hi,
The GL-MT6000 is installed behind an upstream router and works as a VLAN-aware access point. The upstream router provides the VLAN gateway, DHCP server, firewall policy, and Internet access. The MT6000 only bridges VLAN traffic between the wired ports and Wi-Fi SSID.
Below is our topology.
Upstream router
  VLAN 1 / main LAN
  VLAN 20 / gateway + DHCP
        |
        | trunk port
        | VLAN 1 untagged
        | VLAN 20 tagged
        |
GL-MT6000 lan1
  lan2/lan3/lan4 = default LAN
  lan5 = VLAN 20 access port
  SSID VLAN20 = VLAN 20 Wi-Fi access
In this set, wired clients connected to MT6000 lan5 received 192.168.20.x addresses. Wireless clients connected to SSID VLAN20 also received 192.168.20.x addresses.
You can configure it by following the steps below.
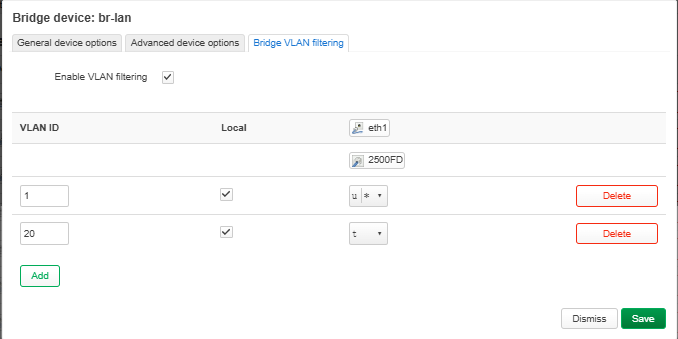
- On the upstream router, configure the port connected to MT6000 lan1 as a trunk port.
Network > Interfaces > Devices > br-lan> Configure > Bridge VLAN filtering.
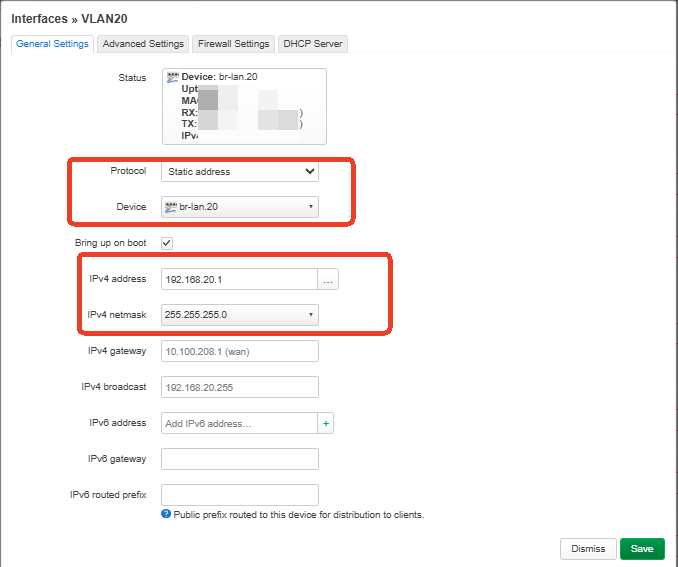
Create a VLAN 20 interface on the upstream router.
Network > Interfaces >Add new interface
Interface: VLAN20
IP address: 192.168.20.1/24
DHCP server: enabled
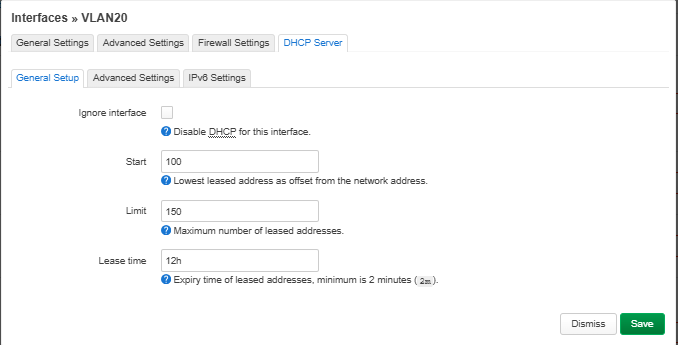
Network >Firewall > Add
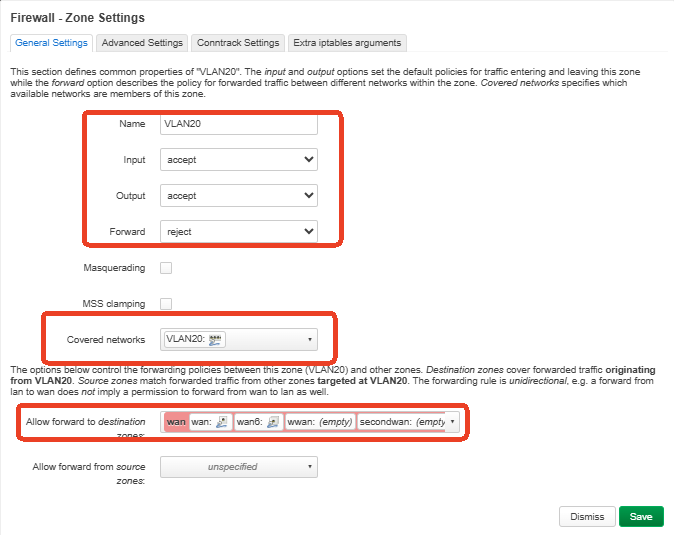
Then save&apply.
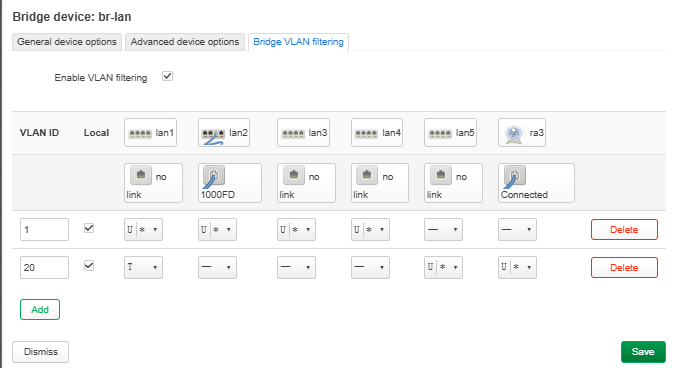
2. On the MT6000, go to `Network > Interfaces > Devices > br-lan > Configure > Bridge VLAN filtering.
Configure VLAN 1 as the default LAN and configure VLAN 20 for the trunk uplink, wired access port, and Wi-Fi SSID.
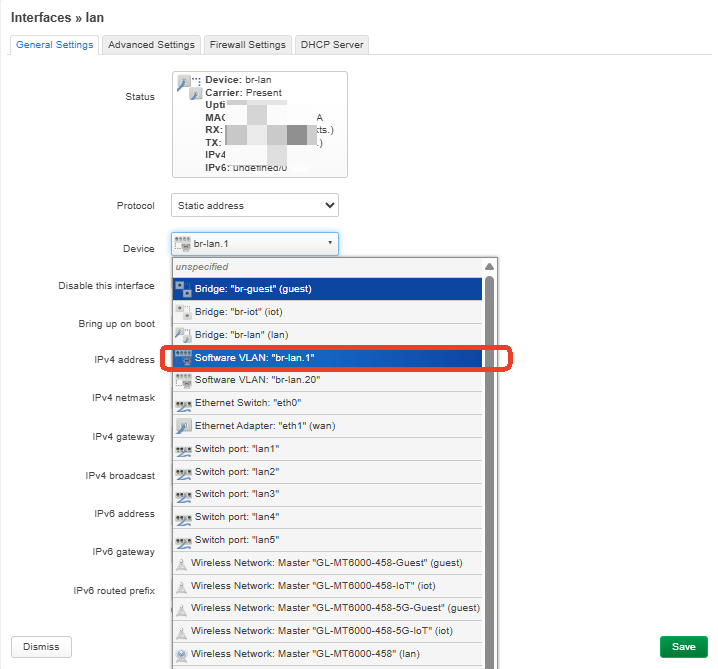
- Interfaces > lan > edit, change br-lan to br-lan.1.
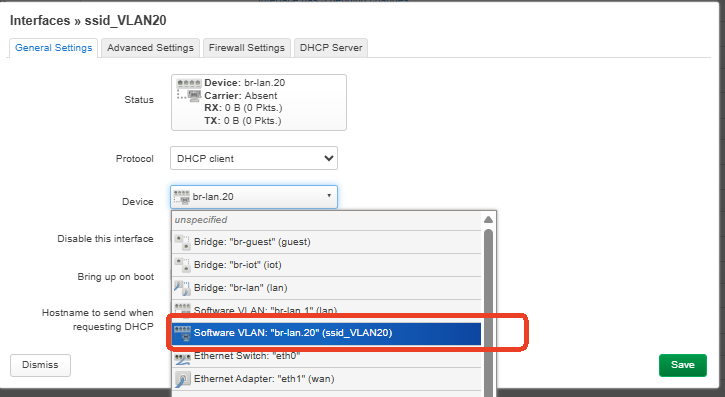
- Create an interface on the MT6000 for VLAN 20.
Name: ssid_VLAN20
Protocol: DHCP client
Device: br-lan.20
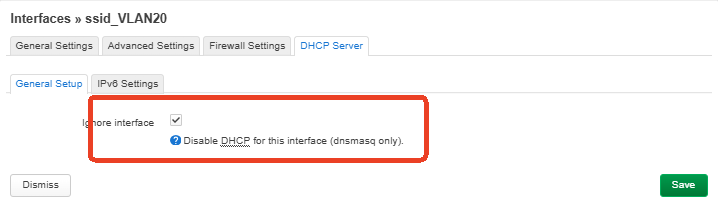
DHCP server: disabled / Ignore interface
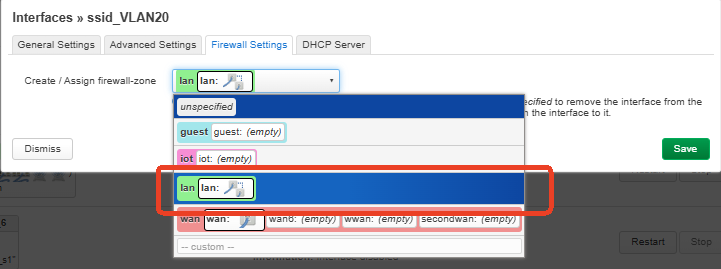
Firewall zone: lan
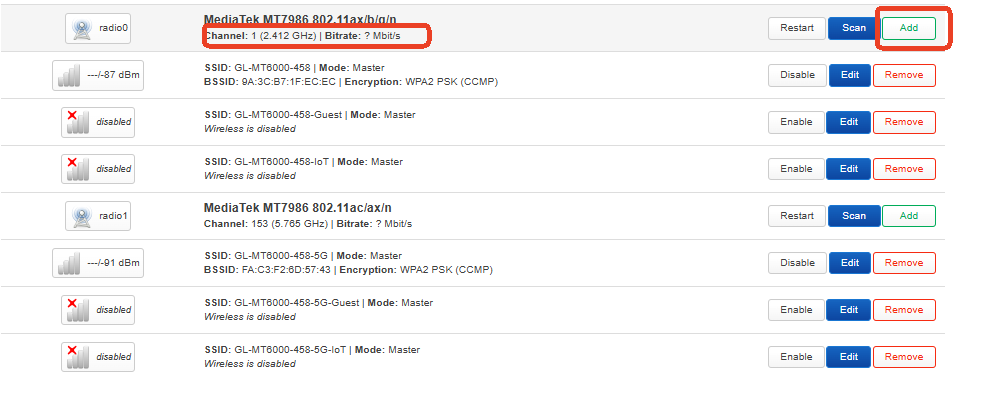
5. Create a new Wi-Fi SSID on the MT6000.
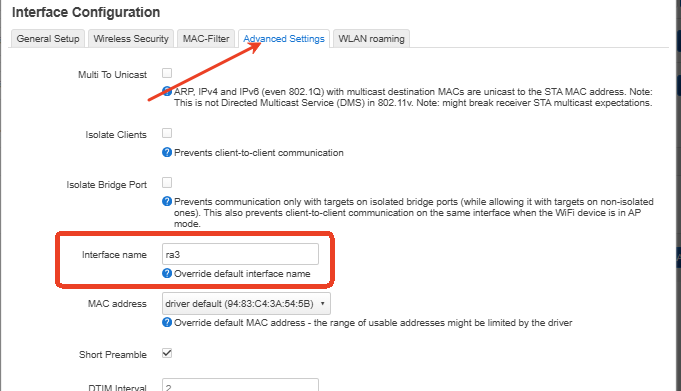
NetWork > Wireless > Edit SSID > Advanced Settings.
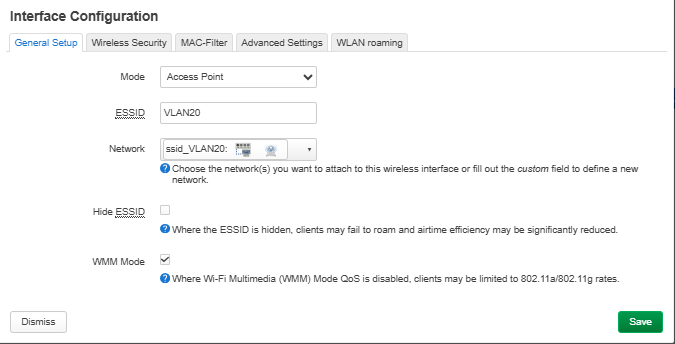
SSID: VLAN20
Mode: Access Point
Network: ssid_VLAN20
Encryption: WPA2-PSK
Interface name: ra3
Save&apply.
After creating the SSID and setting the wireless interface name to ra3, we also need to add ra3 to VLAN 20 as an untagged member.
You can add it by SSH.
uci add_list network.@bridge-vlan[1].ports='ra3:u*'
uci commit network
/etc/init.d/network reload
wifi reload
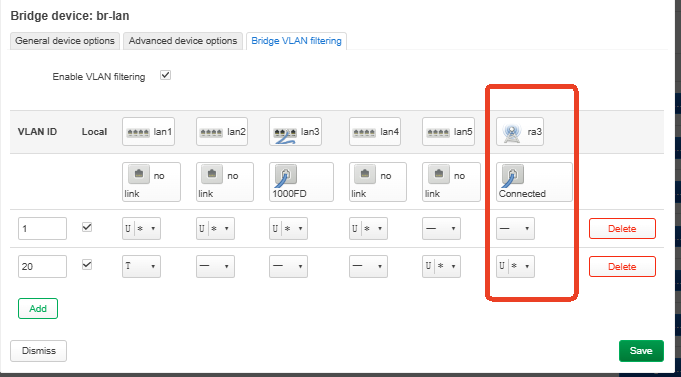
After this, connect MT6000 lan1 to Upstream router(eth1), wireless clients connected to VLAN20 should receive DHCP from the upstream router.
Answers to your questions
1.Yes, testing VLANs in router mode first is useful for basic validation, but the final test should be done with the MT6000 behind the upstream router as a VLAN-aware AP.
2&3.For the example, please refer to the tested configuration above. In our test, the default LAN used br-lan.1, VLAN 20 used br-lan.20, the SSID used interface name ra3, and both wired and wireless VLAN 20 clients received DHCP correctly from the upstream router.
4.One important point is that after creating the SSID with interface name ra3, ra3 must also be added to VLAN 20 as an untagged member.
If you have any questions, please don't hesitate to let us know.