For anyone reading about the new *sshole exploit - even though the page does list "openwrt" as impacted, it does not impact GL routers running the default SSH. The bypass is specific to OpenSSH "sshd" built against musl. GL routers ship with Dropbear ssh. We tested this exploit against a BerylAX (v4.11.0), Beryl 7 (v4.9.0) and SlateAX (v4.8.4) to be sure.
But... if you happen to be the adventurous type that has added OpenSSH openssh-server package via the plugin's directory, that is a musl, non-PAM build, and the disclosure repo reports the bug working back to v 7.5p1.
This is also a great time to check your router's remote access settings.. These are the only proper settings if your GL router is directly exposed to the internet:
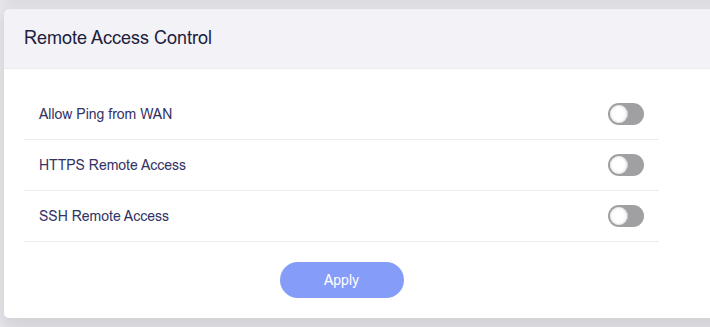
The days of directly exposing SSH to the internet with alt-port, key-auth and fail2ban are behind us. The trusty ssh daemon saw major CVEs this past year, and with AI I'm sure we can expect more to come. With the options of remote access via GoodCloud, Tailscale or ZeroTier built right into the router, there is no need to expose your router's ssh or nginx ports directly to the internet.
PS - for all the homelabbers and cloud VPS peeps - this exploit absoutely hits Alpine hard, which is likely what most your docker containers are running.