On Flint 4, the GL.iNet Admin Panel frontend blocks standalone Top-Level Domains (TLDs) such as ai, io, or gle in the VPN Policy setting page - specifically the Select Target Destination page.
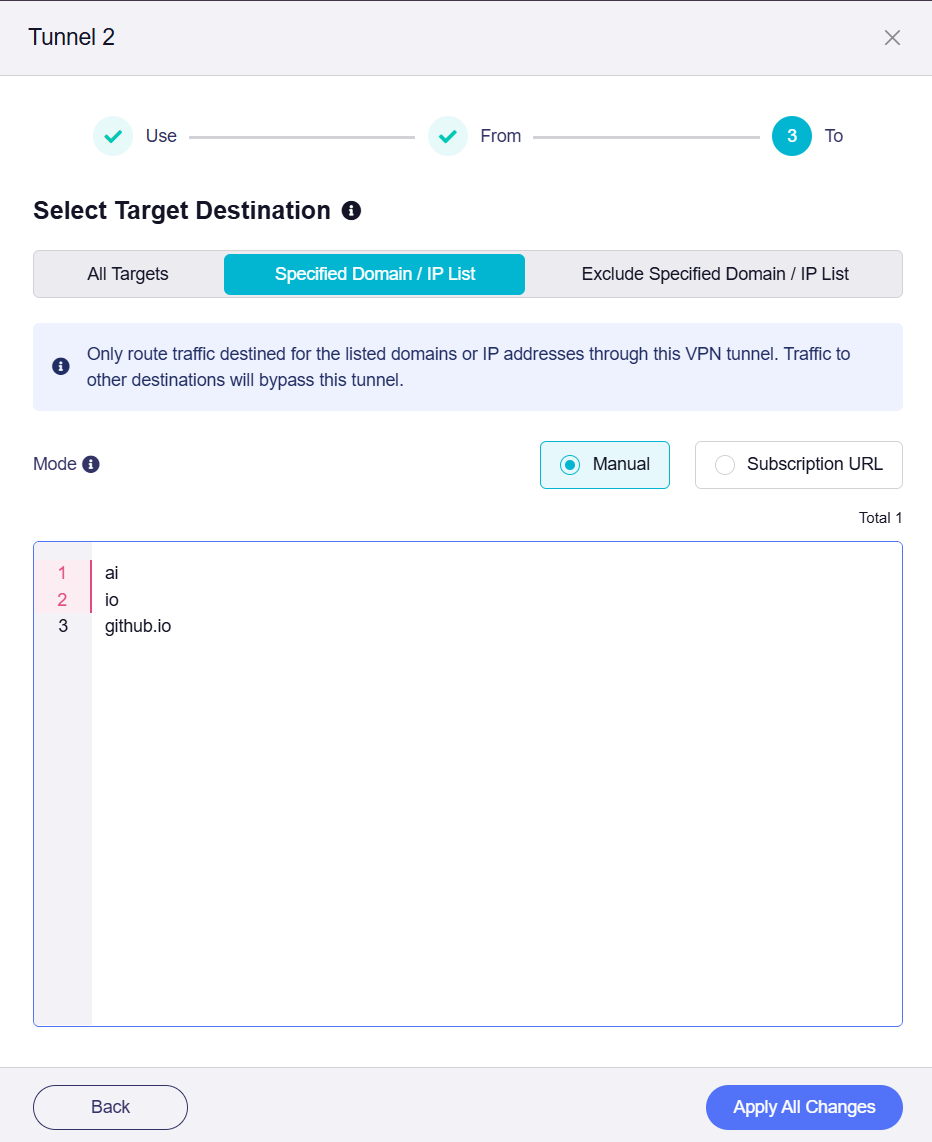
Please consider relaxing the domain validation in the frontend so that TLDs like io, and ai etc. are allowed.
temporary workaround
To route entire TLDs, a temporary workaround is to manually edit the policy file via SSH:
- SSH into the router
- Run
uci show route_policyto locate the policy file, such asroute_policy.@rule[1].to_list_external='/etc/domain_mac_list/dst_net6766' - Edit that file
/etc/domain_mac_list/dst_net6766to include the standalone TLDs, each TLD as a new line; - Then restart the vpn client,
/etc/init.d/vpn-client restart
I have tested with standalone TLDs like ai and gle, and above temporary solution works -
ai and gle are shown in /tmp/dnsmasq.d/via_domains and in the dns_mark dump.
root@GL-BE14000:~# grep -E "/gle/" /tmp/dnsmasq.d/via_domain
nftset=/gle/4#inet#vpn_table#dst_net6766,6#inet#vpn_table#dst_net6766_6
root@GL-BE14000:~# grep -E "/ai/" /tmp/dnsmasq.d/via_domain
nftset=/ai/4#inet#vpn_table#dst_net6766,6#inet#vpn_table#dst_net6766_6

root@GL-BE14000:~# cat /proc/dns_mark/dump | grep -E "^gle"
gle
root@GL-BE14000:~# cat /proc/dns_mark/dump | grep -E "^ai"
ai
muse.ai and c.gle resolved IPs are also added to the IP sets in nftables vpn_table successfully.
Many thanks in advance for the GL.iNet dev team's consideration!
