ot my Flint 3e delivered yesterday, and I’m already thinking about returning it—the update situation seems really sketchy. Version 4.9 added a dedicated IoT network feature, which is the exact reason I bought it. It’s been two months since 4.9 dropped for the Flint 3, and I highly doubt we'll actually see it on the 3e despite GL.iNet's promises.
It is indeed disappointing. The announcement explicitly stated the second quarter, but here we are at the end of July with absolutely no updates. What's worse, even the 4.10.0 beta for Flint 3 is already out. This massive disparity in treatment is honestly infuriating.
flint 3 e[xcluded]
GL-BE6500 Flint 3e ownere here, i’m also curious when 4.9 will be out, at least beta ?
AmneziaWG was updated to 3.0 and amnezia premium offers VLESS too, will be these updated/added ?
Anything new for the Mudi 7 and Slate 7 Pro?
We A1300 users would be freaking happy with just a security update at least, the firmware is over a year old. This is unacceptable for a ‘supported’ device from a company that continues to pump out new devices like crazy, obviously y’all have resources.
Thank you for updating routers, adding new features and trying to keep them stable and secure.
Will the mt-6000 router get mtk firmware with op24 or op25 in the near future?
MTK SDK it's close source (the development base for GL) and op24/op25 uses OSS SDK (open source drivers) so unless MediaTek updates their SDK (close source) with a new openwrt24 or 25 base we don't going to see a MTK SDK op24/25 
This feature would be loved by a lot of Gl.inet Owners I know including myself.
Another Feature which I would love is a additional TOTP 2FA for login into the Routers for more safety!
Ok, thanks for the clarification. So there's little chance of an update from Mediatek? The router was released in November 2023 and the processor in May 2022, so maybe they will make an update?
I agree. Even the default IP address for logging in doesn't use HTTPS!
Hi GL-Inet guys & gals,
In the process of working through this Chrony advice, I’ve discovered that these changes are overwritten on reboot in 4.9b5.
REPRO:
-
ssh gateway
-
uci show chrony
chrony.@server[0]=server
chrony.@server[0].iburst='yes'
chrony.@server[0].disabled='no'
chrony.@allow[0]=allow
chrony.@allow[0].interface='lan'
chrony.@makestep[0]=makestep
chrony.@makestep[0].threshold='1.0'
chrony.@makestep[0].limit='3'
chrony.@nts[0]=nts
chrony.@nts[0].rtccheck='yes'
chrony.@nts[0].systemcerts='yes'
chrony.@pool[0]=pool
chrony.@pool[0].maxpoll='12'
chrony.@pool[0].iburst='yes'
chrony.@pool[0].nts='yes'
chrony.@pool[0].hostname='time.cloudflare.com'
chrony.time_nl=server
chrony.time_nl.hostname='ntppool1.time.nl'
chrony.time_nl.iburst='yes'
chrony.time_nl.nts='yes'
chrony.netnod=server
chrony.netnod.hostname='nts.netnod.se'
chrony.netnod.iburst='yes'
chrony.netnod.nts='yes'
chrony.ptb=server
chrony.ptb.hostname='ptbtime1.ptb.de'
chrony.ptb.iburst='yes'
chrony.ptb.nts='yes'
chrony.dfm=server
chrony.dfm.hostname='time.dfm.dk'
chrony.dfm.iburst='yes'
chrony.dfm.nts='yes'
chrony.cifelli=server
chrony.cifelli.hostname='time.cifelli.xyz'
chrony.cifelli.iburst='yes'
chrony.cifelli.nts='yes' -
uci -q delete chrony.@pool[0]
uci -q delete chrony.time_nl
uci -q delete chrony.netnod
uci -q delete chrony.ptb
uci -q delete chrony.dfm
uci -q delete chrony.cifelliuci add chrony pool
uci set chrony.@pool[-1].maxpoll='12'
uci set chrony.@pool[-1].iburst='yes'
uci set chrony.@pool[-1].nts='yes'
uci set chrony.@pool[-1].hostname='2.us.pool.ntp.org'
uci set chrony.@makestep[0]='makestep'
uci set chrony.@makestep[0].threshold='1.0'
uci set chrony.@makestep[0].limit='3' -
uci commit chrony
-
/etc/init.d/chronyd restart
-
uci show chrony
chrony.@server[0]=server
chrony.@server[0].iburst='yes'
chrony.@server[0].disabled='no'
chrony.@allow[0]=allow
chrony.@allow[0].interface='lan'
chrony.@makestep[0]=makestep
chrony.@makestep[0].threshold='1.0'
chrony.@makestep[0].limit='3'
chrony.@nts[0]=nts
chrony.@nts[0].rtccheck='yes'
chrony.@nts[0].systemcerts='yes'
chrony.@pool[0]=pool
chrony.@pool[0].maxpoll='12'
chrony.@pool[0].iburst='yes'
chrony.@pool[0].nts='yes'
chrony.@pool[0].hostname='2.us.pool.ntp.org' -
cat /etc/config/chrony
config server
option iburst 'yes'
option disabled 'no'config allow
option interface 'lan'config makestep
option threshold '1.0'
option limit '3'config nts
option rtccheck 'yes'
option systemcerts 'yes'config pool
option maxpoll '12'
option iburst 'yes'
option nts 'yes'
option hostname '2.us.pool.ntp.org' -
-
ssh gateway
-
uci show chrony
<as in #2> -
cat /etc/config/chrony
config server
option iburst 'yes'
option disabled 'no'config allow
option interface 'lan'config makestep
option threshold '1.0'
option limit '3'config nts
option rtccheck 'yes'
option systemcerts 'yes'config pool
option maxpoll '12'
option iburst 'yes'
option nts 'yes'
option hostname 'time.cloudflare.com'config server 'time_nl'
option hostname 'ntppool1.time.nl'
option iburst 'yes'
option nts 'yes'config server 'netnod'
option hostname 'nts.netnod.se'
option iburst 'yes'
option nts 'yes'
config server 'ptb'
option hostname 'ptbtime1.ptb.de'
option iburst 'yes'
option nts 'yes'config server 'dfm'
option hostname 'time.dfm.dk'
option iburst 'yes'
option nts 'yes'config server 'cifelli'
option hostname 'time.cifelli.xyz'
option iburst 'yes'
option nts 'yes'
Who knows.... 

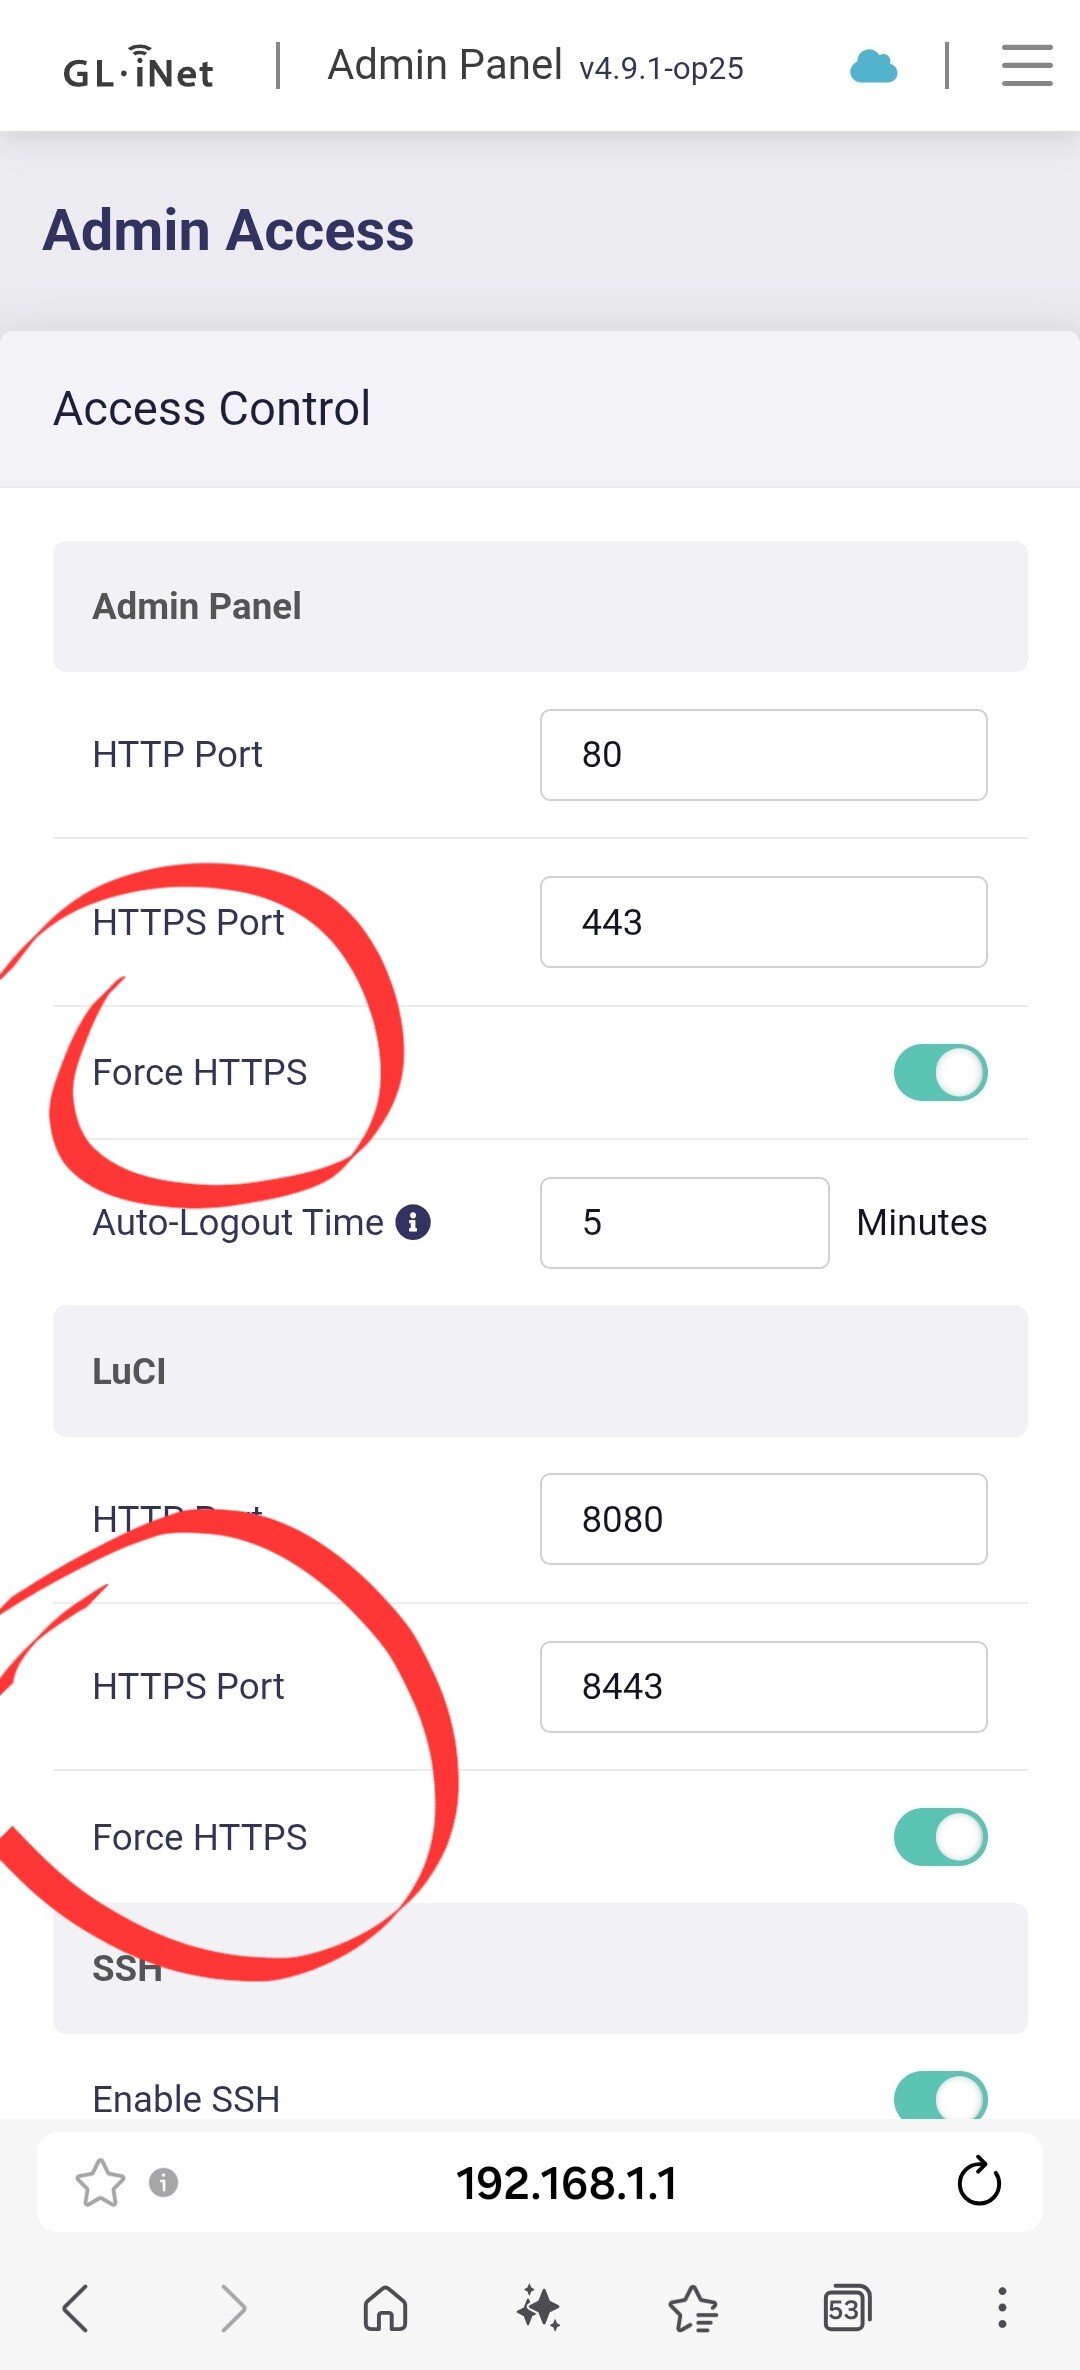
Thanks! I just tried it, but it doesn't work on Firefox. https://192.168.8.1/ just fails to load the login page.
I've been playing with v4.9 for a little while now and decided to try out other feature like the new IoT network.
What does the orange triangle with a white exclamation mark mean? I have policy-based routing enabled with the enhanced kill switch enabled. I noticed that from time to time, especially if I reboot the router, my devices like phones will get a new MAC address and then lose internet access. As a result, I reserve an IP for most of my devices. I noticed that if a device on the IoT network has a reserved IP, I get the orange triangle next to the Reserved IP toggle, and the device has no internet in the VPN tunnel. Why?
What are the benefits of enabling auto remove offline clients?
With regards to the Guest and IoT networks, I notice there are fewer options to set compared to the main network. Do the Guest and IoT networks use the radio configuration settings from the main network, like bandwidth and channel?
Both Guest and IoT networks seem to have AP isolation enabled by default. Is there any benefit to enabling that for LAN too?
For the DPI data statistics, will there be an option to see a month and a year? Right now, the longest duration is a week.
Is SQM necessary if I am on a symmetrical gigabit fiber internet connection? In what situation will SQM be necessary?
@knee_mountain523
I think only two of your questions really require input from the GL.iNet developers:
-
The orange warning icon together with the VPN connectivity issue (this could indicate a firmware bug).
-
Whether monthly/yearly DPI statistics are planned (only the developers can answer the roadmap).
The other questions are mostly general networking topics that are well documented and can easily be answered by ChatGPT or another AI, for example:
-
What SQM is and when it is useful.
-
What AP isolation does.
-
What "Auto Remove Offline Clients" is for.
-
How Guest and IoT SSIDs inherit the radio settings from the main Wi-Fi.
The developers' time is probably better spent investigating bugs and implementing new features than answering generic networking questions.
For future posts, it would be great if you could first ask an AI or check the documentation for these kinds of general questions, and then bring the remaining GL.iNet-specific issues to the forum. That would help keep the developers focused on the things only they can answer.
I just tried to do a speed test, and maybe I'm doing something wrong, but devices on the main network are much faster than on the guest and IoT networks. What latency should I expect on fast.com? I'm currently getting the following: Unloaded - 16ms, Loaded - 787ms.
What's the reason for that?