DNS hijack rules are only generated for lan/guest/iot — custom VLAN bridges leak in cleartext (4.9.1)
GL-BE14000, firmware 4.9.1. Reporting a DNS leak that the web UI gives no indication of.
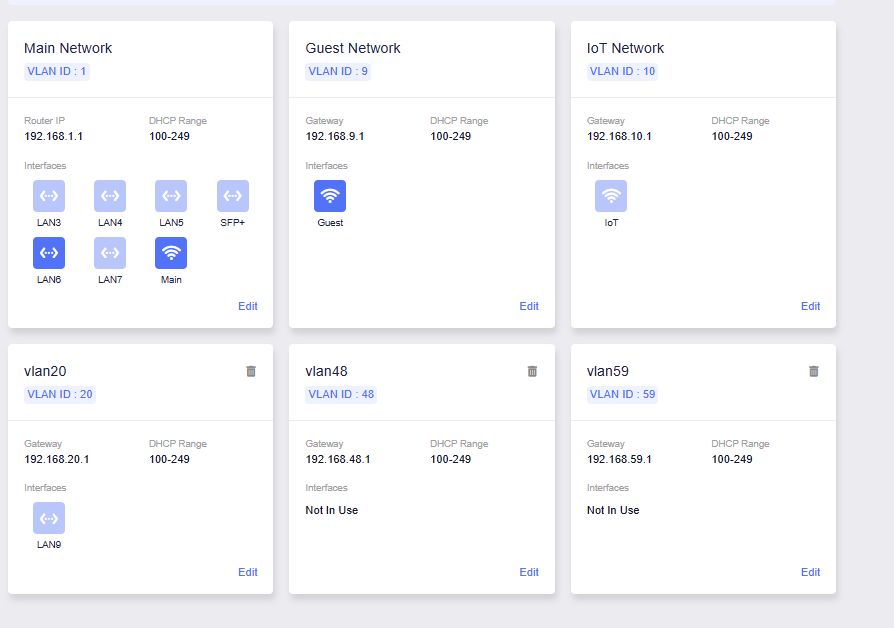
Setup: WireGuard client with a domain-based VPN policy, AdGuard Home enabled (Handle client requests OFF), and a custom VLAN interface vlan59 added via LuCI with its own firewall zone.
Issue 1 — Override DNS Settings for All Clients does not cover custom bridges.
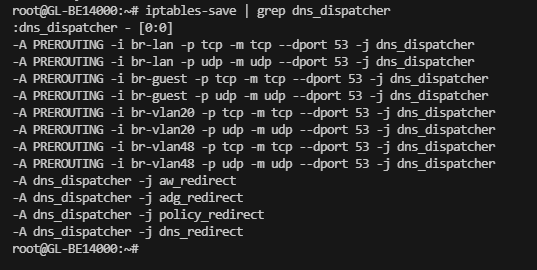
With that option enabled, the generated PREROUTING rules are:
-A PREROUTING -i br-lan -p udp --dport 53 -j dns_dispatcher
-A PREROUTING -i br-guest -p udp --dport 53 -j dns_dispatcher
-A PREROUTING -i br-iot -p udp --dport 53 -j dns_dispatcher
br-vlan59 is absent, even though it has a proper firewall zone in /etc/config/firewall. Three devices on that VLAN with hardcoded 8.8.8.8 were sending cleartext DNS straight out the WAN — 654 concurrent conntrack entries, SNAT'd to my real WAN IP. AdGuard Home never saw them, and neither did the tunnel. Nothing in the UI indicates the option's coverage is limited to the three built-in zones.
Issue 2 — AdGuard Home upstream DoT intermittently egresses via WAN.
With Services from GL.iNet Use VPN irrelevant here (AdGuard runs as gid 20000 and is matched by TUNNEL*_LOCAL_POLICY), the marking rule works — 310 packets matched. But long-lived DoT sockets created before the policy loads keep their original route. Measured 4 of 13 upstream connections to 1.0.0.1 / 8.8.4.4 egressing via WAN with the real IP, hours after boot. The per-tunnel Kill Switch does not catch this: its DROP rule sits in the same chain behind a MARK rule that always matches first, so its counter stays at 0.
Note for anyone writing their own guard rule: matching on ! -o wgclient1 in filter OUTPUT does not work. At that point the packet still carries the pre-reroute output interface, so the rule matches everything and takes DNS down completely (I did this — 285 rejects, total resolution failure). Match the fwmark instead:
iptables -A output_rule -p tcp --dport 853 -m mark ! --mark 0x1000/0xf000 -j REJECT --reject-with tcp-reset